Secure Pipeline: Security-First CI/CD
Eight automated security scan stages aggregated into DefectDojo, covering SAST, SCA, secrets, and SBOM on every push, for ~$5/month.
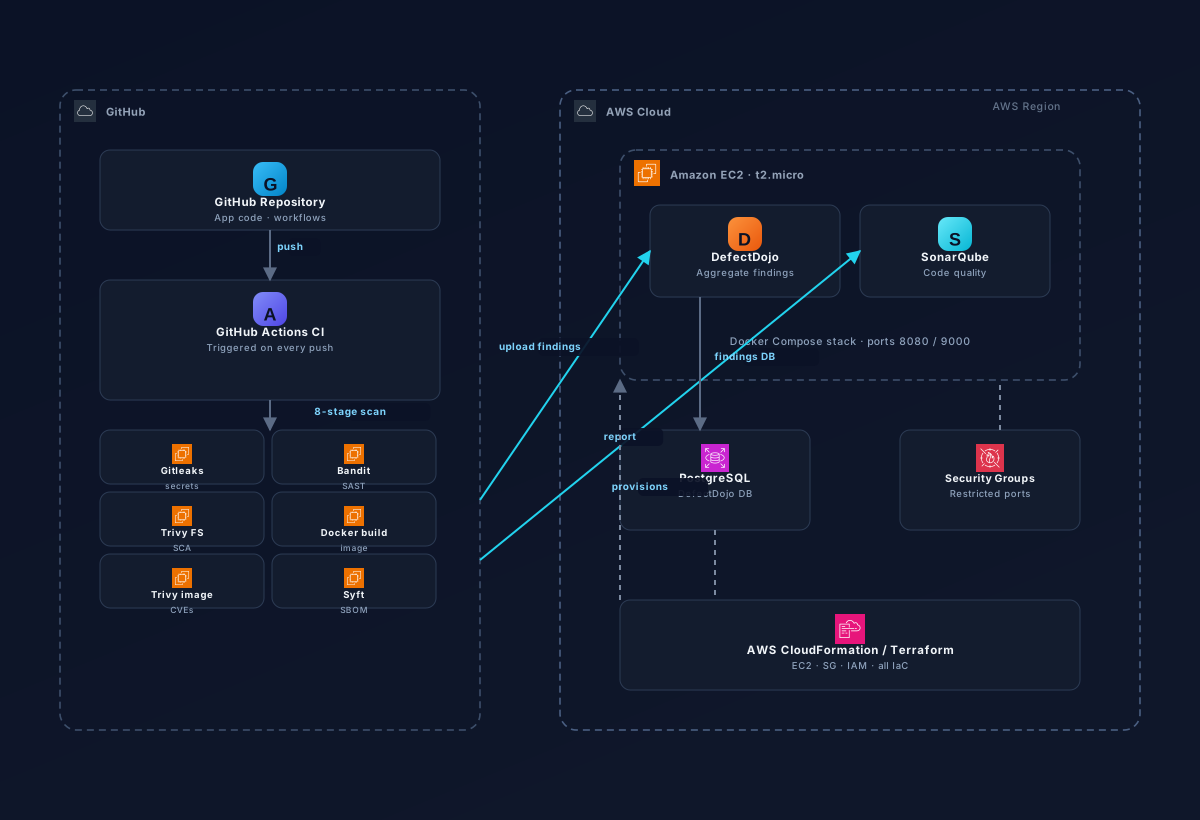
- Security scan stages
- 8
- Security scan stages
- Tools integrated
- 5+
- Tools integrated
- Monthly cost
- ~$5
- Monthly cost
Overview
A security-first CI/CD pipeline that runs eight stages of automated security scanning on every push, aggregates all findings in DefectDojo, and integrates with SonarQube for code quality analysis. The entire infrastructure is provisioned via Terraform on AWS EC2, free-tier eligible.
Pipeline Stages
| Stage | Tool | What It Finds |
|---|---|---|
| Stage 1 | Gitleaks | Hardcoded secrets, API keys, passwords |
| Stage 2 | Bandit | Python security bugs (eval, injection, unsafe calls) |
| Stage 3 | Trivy FS | Vulnerable dependencies, misconfigurations |
| Stage 4 | Docker Build | Container image build |
| Stage 5 | Trivy Image | OS-level CVEs in container layers |
| Stage 6 | Syft SBOM | CycloneDX software bill of materials |
| Stage 7 | SonarQube | Code quality bugs, security hotspots |
| Stage 8 | DefectDojo | Aggregates all findings in one dashboard |
Architecture
Infrastructure
A single AWS EC2 instance (t2.micro, free-tier) hosts both DefectDojo and SonarQube via Docker Compose, provisioned entirely through Terraform. The CI pipeline connects to this instance using repository secrets.
- Terraform: Provisions EC2, security groups, and SSH access
- Docker Compose: Runs DefectDojo + SonarQube + PostgreSQL
- GitHub Actions: Triggers on push, runs all scanners, uploads results
- Dependabot: Automatic dependency update PRs
Key Features
- SAST + SCA + Secrets: Covers static analysis, software composition analysis, and secret detection in a single pipeline
- SBOM Generation: Syft produces a CycloneDX bill of materials for supply chain transparency
- Centralized Dashboard: DefectDojo aggregates findings from all tools into one view
- SonarQube Integration: Bandit results are imported into SonarQube security tab alongside quality metrics
- Free-Tier: Entire infrastructure runs within AWS Free Tier (~$5/month)
Tools Breakdown
Bandit
Python security linter that scans source code for common vulnerabilities: SQL injection, unsafe eval/exec, hardcoded passwords, and insecure file permissions. Results go to both DefectDojo and SonarQube.
Gitleaks
Scans git history and working tree for hardcoded secrets before they reach the repository. Configured via .gitleaks.toml with custom allowlists and regex patterns.
Trivy
Three-in-one scanner: filesystem scanning for dependency vulnerabilities (requirements.txt), secret scanning for exposed keys, and container image scanning for OS-level CVEs.
DefectDojo
The central aggregation point. Instead of checking five separate reports, all findings from every scanner are uploaded to DefectDojo's single dashboard for triage and tracking.
Like what you're seeing?
I'm always up for tackling challenging infrastructure, automation, and AI/DevOps problems. Let's build something together.